
In a shocking revelation, Ledger announced on October 10 that one of its hardware wallets, belonging to a customer, was found to contain an unauthorized implant. This alarming discovery arises amid ongoing investigations into a series of thefts associated with the Southeast Asian reseller CryptoBilis.
Initial estimates of the total losses from the incident range from $72 million to $93.4 million, although Ledger has not yet verified any specific figures. The company assured users that its security infrastructure and systems remain intact and that it is actively contacting affected customers while collaborating with law enforcement.
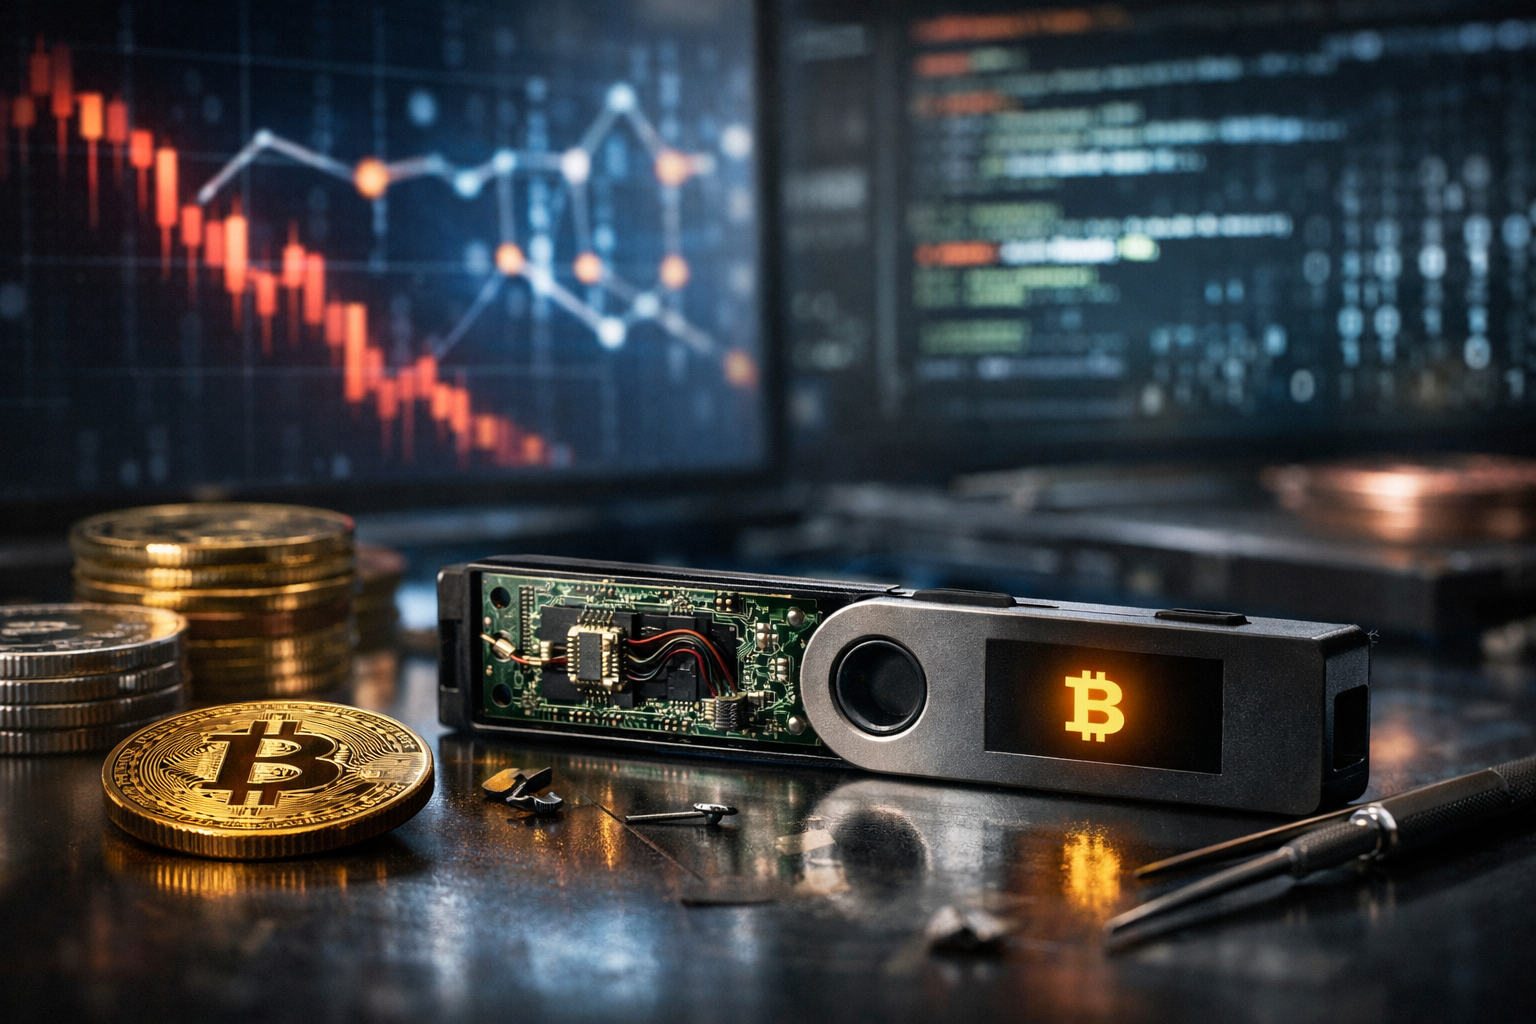
“One of the impacted users’ devices contained an unauthorized hardware implant,” Ledger stated, marking the first confirmation of physical tampering related to its products. Such revelations have raised serious concerns among users regarding the integrity of hardware wallets, which are often considered a secure option for storing cryptocurrencies.
Investigation Findings
As the investigation unfolds, various on-chain investigators have reported staggering figures concerning the suspected thefts. Yfarmx estimated losses at $93.4 million across 471 addresses, while Bitquery suggested a slightly lower figure of $92.9 million across 311 addresses. Another researcher, Specter, claimed that losses surpassed $86 million.
On-chain investigator tanuki42 highlighted that over $72 million had been transferred to addresses linked to the thefts. However, Ledger has yet to provide confirmation on these estimates, and the exact number of affected wallets remains unknown.
Former Mt. Gox CEO Mark Karpelès shared findings concerning a modified Ledger Nano X, which allegedly included a hidden circuit board and cellular equipment capable of intercepting recovery phrases. This equipment purportedly monitored data displayed on the device’s screen during setup, potentially sending sensitive recovery words over a cellular connection. As of now, investigators have not confirmed whether all compromised wallets contained similar components.
In response to the investigation, CryptoBilis, which operates in Indonesia, Malaysia, and the Philippines, has ceased the sale of hardware wallets until the situation is thoroughly examined. Ledger requested this halt on October 9, advising customers who purchased devices from the reseller within the last 90 days to refrain from setting them up. Users who have already configured their wallets are urged to transfer their assets to a new Ledger device with a fresh seed.
Ledger is reportedly working on enhancing its anti-tampering measures and has expressed gratitude to SEAL 911 for their assistance in the investigation. Several users have taken to social media, questioning whether Ledger would offer refunds to victims, especially given that CryptoBilis was an authorized reseller. As of now, Ledger has not announced any plans for compensation.
Emerging Phishing Threats
In a related incident, security researcher Cyber Scrilla alerted the community to a fake Ledger website that appeared prominently in Google search results. This fraudulent site reportedly attempted to deceive visitors into disclosing their 24-word recovery phrases.
The site allegedly received over 1 million visits within a 30-day period, although this figure has yet to be confirmed. A previous report by Zscaler indicated a similar scheme involving misleading Google ads, highlighting the ongoing threats faced by cryptocurrency users.
Ledger strongly advises its users never to enter recovery phrases into websites, apps, or online forms. The company encourages downloading its software exclusively from its official website and meticulously checking web addresses for authenticity.
As the investigation progresses, Ledger’s latest update confirms that at least one device contained an unauthorized implant. However, the total number of tampered devices and the identities of those responsible for the breach remain undetermined.

